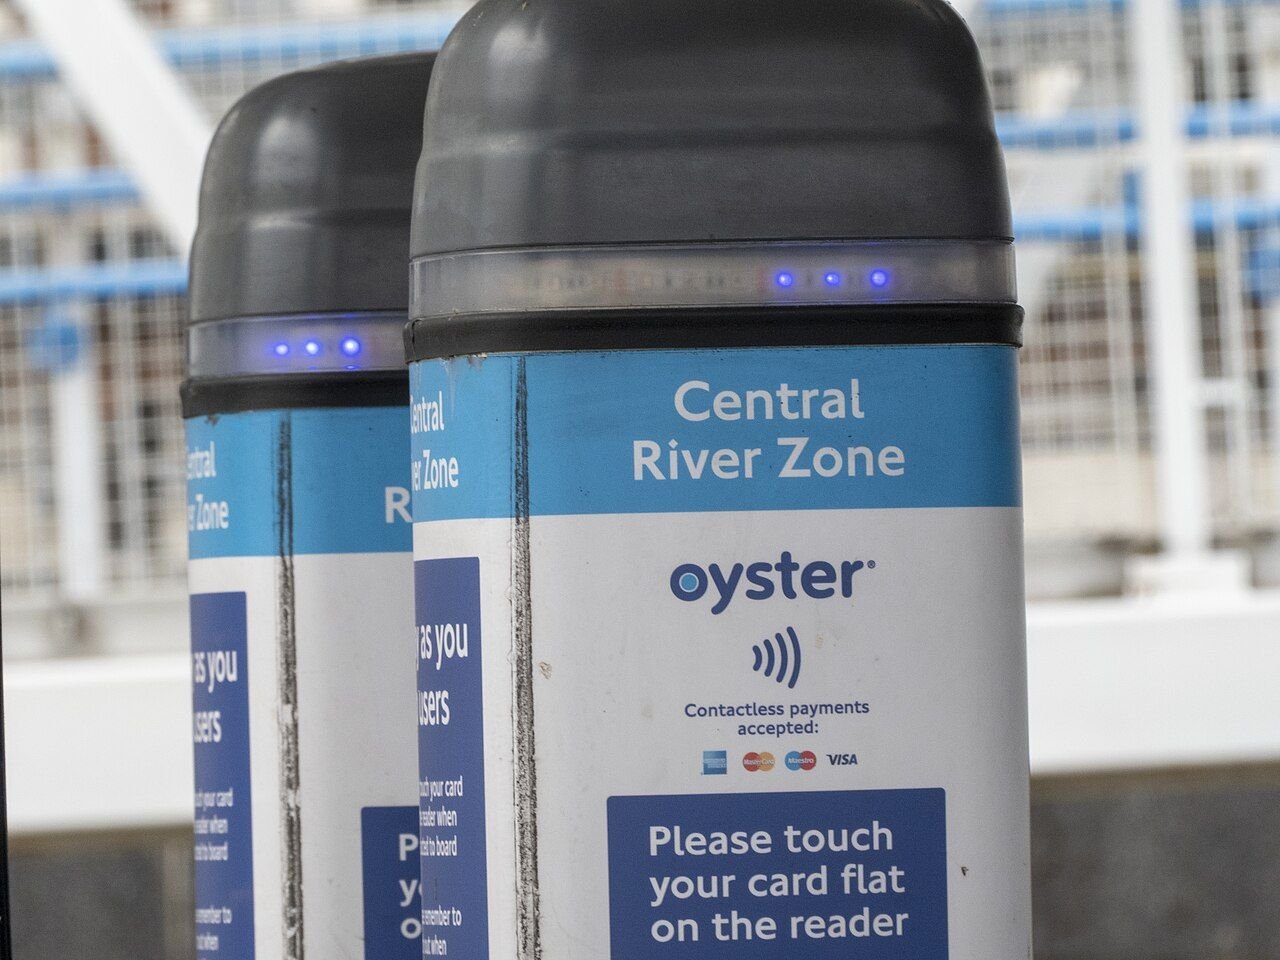
Transport for London has taken its Oyster photocard website offline after a data breach exposed the personal information of approximately 265,000 passengers in the capital.
TfL said it first became aware of the problem on Monday, November 16, when Oyster photocard customers began receiving unexpected emails asking them to create or validate accounts they already held. The emails came from TfL's own systems but were generated as a result of the compromise. "We immediately took the TfL photocard website down while this was being investigated," said Shashi Verma, TfL's director of technology strategy and revenue. "The protection of personal information is a priority for us, and I apologise to our customers affected by this incident."
The information accessed is understood to include names, email and home addresses, phone numbers, dates of birth and security questions and answers. TfL said passwords, bank and payment card details and journey information were not compromised, and it believes the names and dates of birth of children holding Zip Oyster cards were unaffected. Affected account holders include children and students, Londoners aged 60 and over, military veterans, apprentices and care leavers.
TfL said it has contained the incident, contacted customers who may be affected and notified the Information Commissioner's Office. It has found no evidence so far that the compromised data has been used, and it has not disclosed how the attackers got into its systems. Existing photocards still work at ticket barriers, but customers who need to renew a card or check journey history must contact TfL customer services by telephone on 0343 222 1234 while the website remains offline.
Although passwords were not taken, TfL will ask photocard customers to change theirs, along with their security questions and answers, and anyone who reuses those details elsewhere is advised to change them there too. Customers were also warned to watch for suspicious emails, calls or texts. "Security questions are reused across multiple accounts," said Muhammad Yahya Patel, a cyber security adviser at Huntress. "Someone who knows your mother's maiden name or your first pet now potentially has a key that works on more than just your Oyster account."
It is the second major breach at TfL in just over two years. In September 2024, attackers linked to the Scattered Spider cybercrime crew accessed systems holding data on about 10 million people. Verma said the compromised photocard system had been subject to cyber security testing within the past 12 months and that the speed of TfL's response limited the impact this time, while acknowledging that new hacking tools are constantly emerging. "This is a very difficult game to keep up with," he said. TfL said it hopes to restore the website as soon as possible, but gave no date.